01 / 05
Technical risk assessment
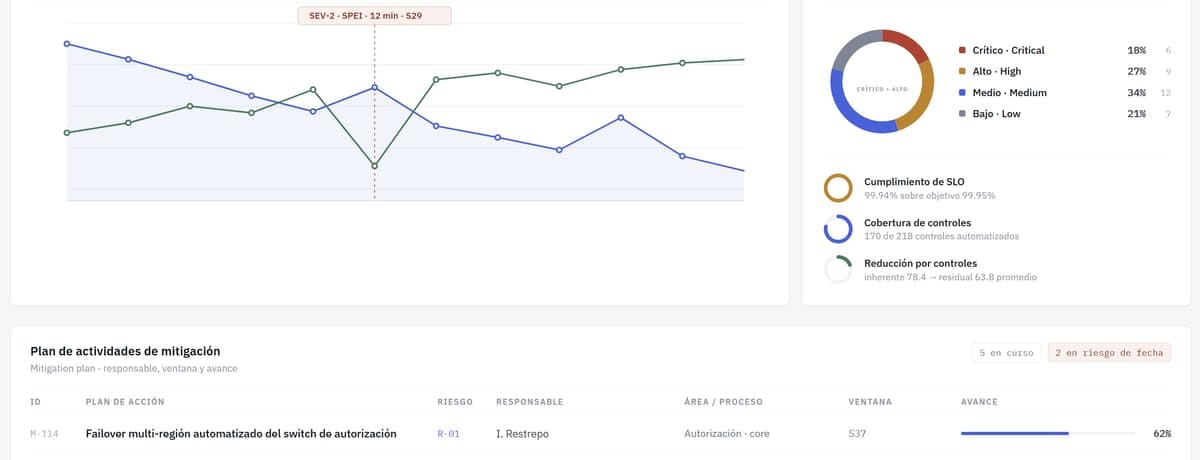
A bounded review, with an end date, that delivers a risk matrix: what can fail, what it costs the operation when it does, and what should be done about it — with an owner and a deadline on every line. It is the place to start when there are more questions than certainties. Compliance is reviewed as an architectural risk, not as a checklist run just before the audit.
- Compliance: where the current design exposes you to penalties or transaction blocks.
- Data integrity: where transactions are lost and where the books stop matching.
- Availability: what interrupts the operation, how often and for how long.
- Technical debt and performance: what makes every change expensive, and what degrades as volume grows.
What you take awayA prioritised risk matrix and a remediation roadmap, with an owner and a deadline on every line.